Artificial intelligence is quickly becoming part of everyday business operations, from customer service and software development to analytics and decision-making. But as AI adoption grows, so do security, privacy, and governance risks.
For business leaders, securing AI should begin with accountability and clear governance. Organizations need to know which AI systems they use, what data those systems access, and who is responsible for managing their risks. NIST’s AI Risk Management Framework highlights governance, risk mapping, measurement, and ongoing management as key parts of responsible AI security.
Key Priorities for Leaders
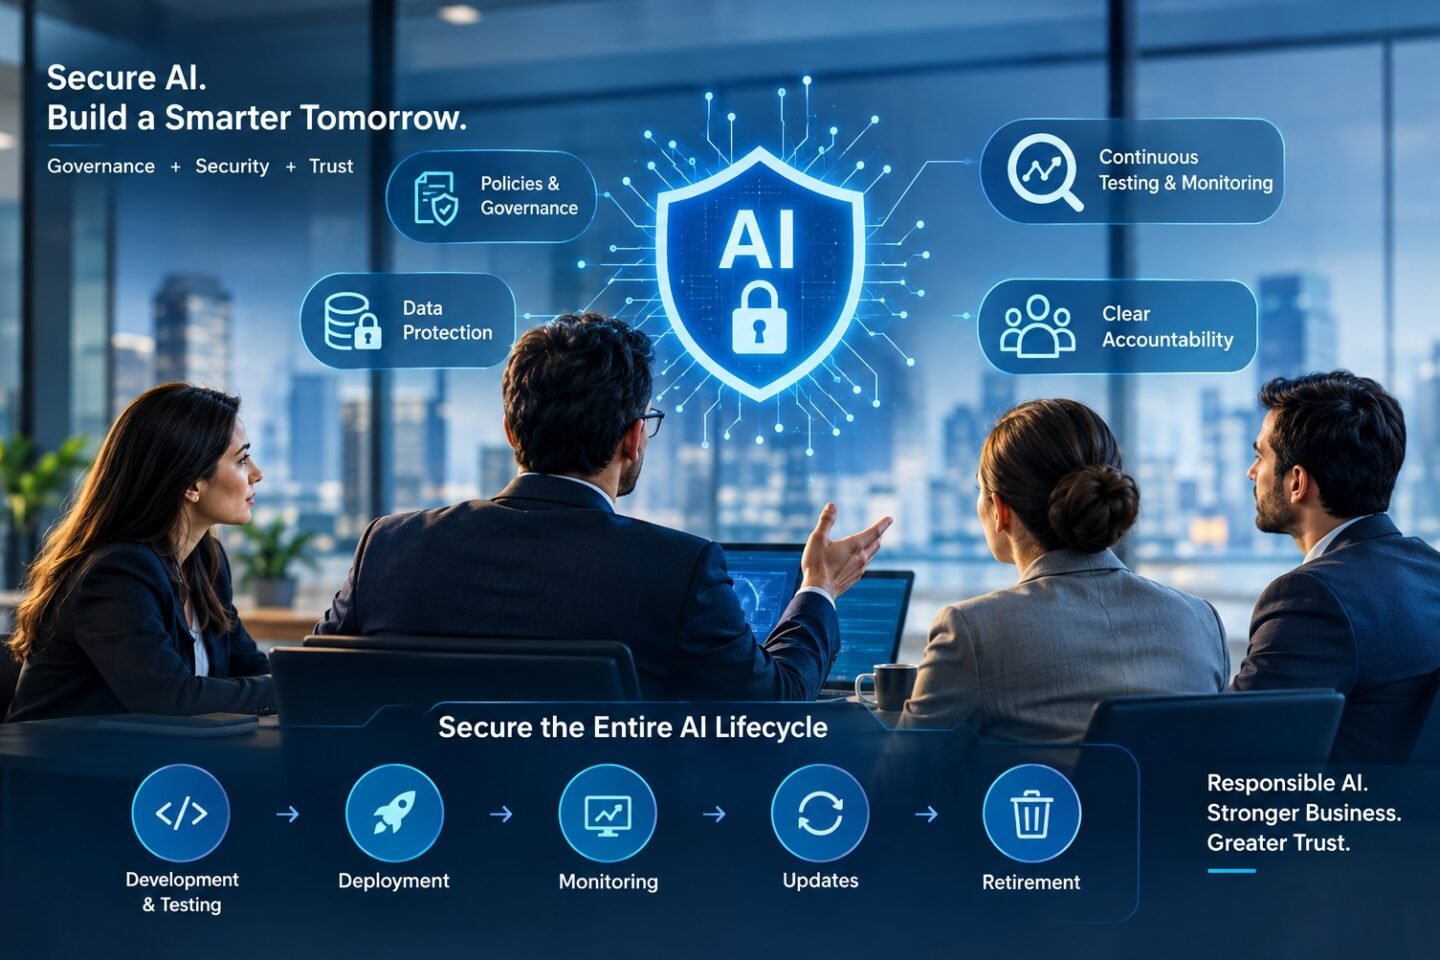
1. Establish clear AI policies
Define how employees can use AI, what information can be shared with AI systems, and which applications require additional security controls.
2. Protect sensitive data
AI tools may process confidential business, customer, or employee information. Strong access controls, data protection, and vendor oversight are essential.
3. Test AI systems regularly
Security should not stop after deployment. AI systems need continuous monitoring, testing, and review as models, data, and threats change.
4. Make accountability clear
Senior leadership should understand AI risks and ensure teams have the authority, resources, and expertise needed to manage them.
5. Secure the entire AI lifecycle
Security should be considered from development and testing through deployment, monitoring, updates, and eventual retirement.
The Bottom Line
AI security is no longer only an IT responsibility. It is a leadership issue that requires clear policies, responsible data management, continuous testing, and executive oversight. By building security into AI strategy from the beginning, organizations can adopt new AI capabilities while managing the risks that come with them.