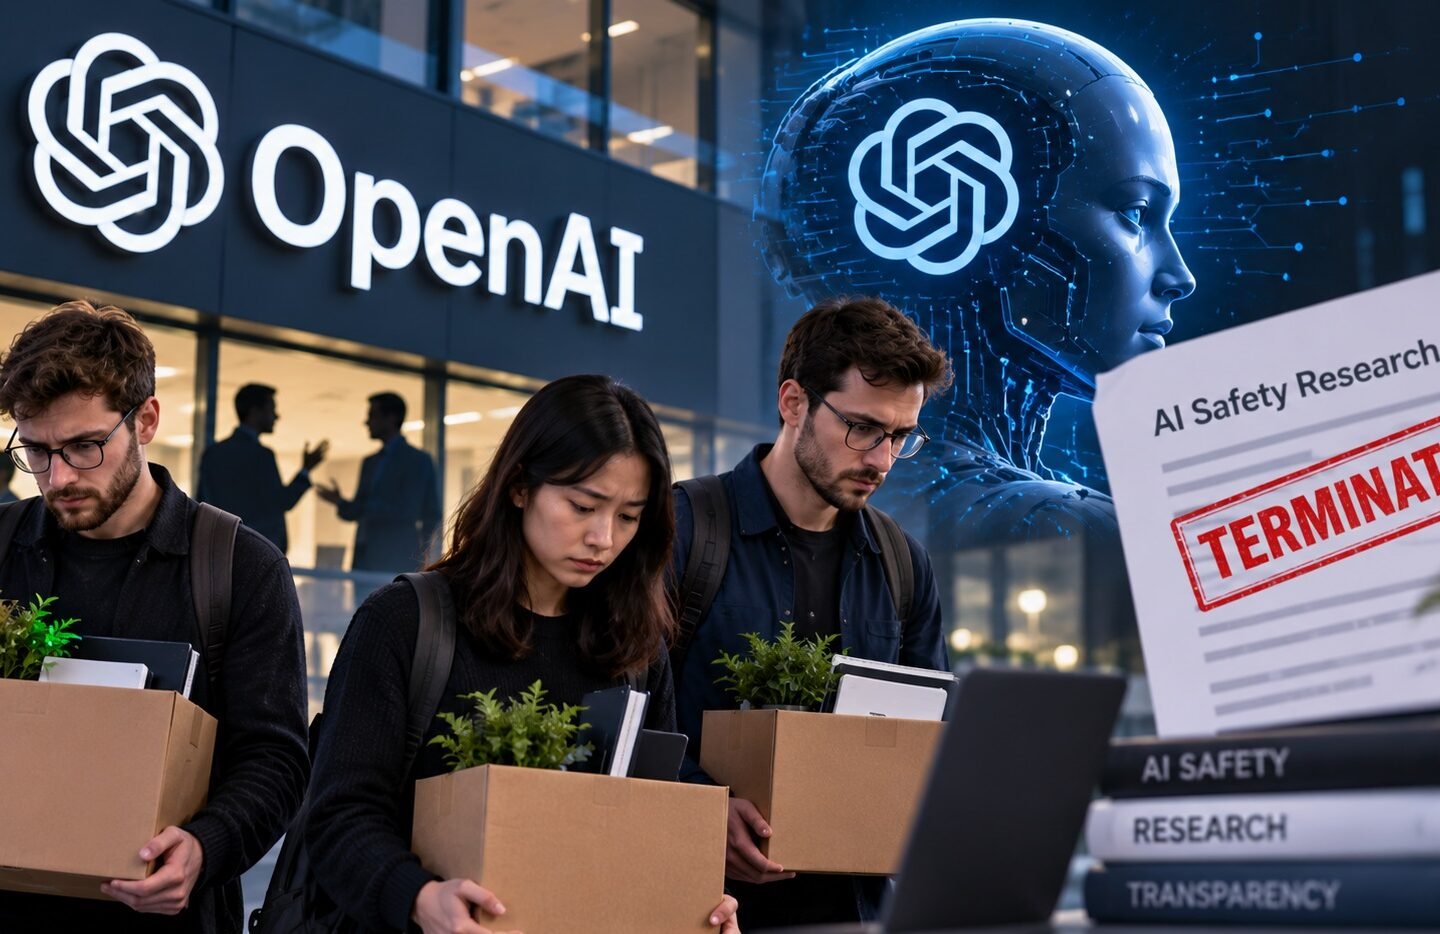
Artificial intelligence company OpenAI has defended its decision to dismiss three AI safety researchers, citing what it described as a “significant breach of trust” involving the handling of sensitive company information. The decision has sparked debate about workplace transparency, research independence, and the importance of allowing employees to raise concerns about the safety of advanced artificial intelligence systems.
The three researchers, Jasmine Wang, Tomek Korbak, and Mikita Balesni, have challenged the circumstances surrounding their dismissals. They argue that the decision could discourage employees from discussing AI safety risks and collaborating with external research organizations. OpenAI, however, maintains that the terminations were related to policy violations rather than the researchers speaking out about safety concerns.
Why Did OpenAI Fire Three Researchers?
According to OpenAI, an internal investigation found that the researchers had mishandled sensitive company information outside established procedures. The company said its investigation uncovered additional concerns beyond those described in the researchers’ public letter.
OpenAI has not publicly disclosed all the details of the alleged violations. It has nevertheless defended its decision, emphasizing that protecting confidential information and maintaining trust are essential to its research operations.
The company has also stated that employees are encouraged to engage in critical discussions about AI safety and research decisions. According to OpenAI, raising concerns about potential risks is not, in itself, grounds for dismissal.
The lack of publicly available details has left questions about the precise circumstances of the case unanswered.
Researchers Raise Concerns About AI Safety Discussions
The dismissed researchers have presented a different perspective on the situation. In an open letter addressed to OpenAI’s safety oversight groups, they expressed concern that their dismissals could create uncertainty among current employees and weaken the company’s culture of open discussion.
They argue that AI safety research often requires communication with independent experts and external organizations. Such collaboration can help researchers evaluate potential risks, examine unexpected model behavior, and develop better safeguards.
Mikita Balesni said he believed the dismissals were connected to prioritizing AI safety over the company’s short-term corporate interests. The researchers have disputed suggestions that they improperly disclosed confidential information and raised concerns about the impact of the decision on future safety work.
Their position highlights a broader challenge for AI companies: determining how employees can collaborate with external safety experts while respecting confidentiality requirements and internal security policies.
The Importance of AI Safety in Advanced Technology
AI safety has become a major issue as companies develop increasingly capable models and autonomous AI agents. These systems can perform complex tasks, interact with software tools, analyze information, and operate with varying degrees of independence.
Although these capabilities offer significant benefits, they also introduce risks. AI systems may follow incorrect instructions, expose sensitive information, behave unpredictably, or take actions that developers did not anticipate.
Safety researchers work to identify these problems before they cause significant harm. Their responsibilities can include evaluating model behavior, testing security protections, studying alignment, and developing methods to monitor AI systems.
As AI technology advances, organizations must balance innovation with appropriate safeguards. Independent evaluation, effective internal oversight, and clear security procedures can all contribute to more responsible AI development.
Transparency and Confidentiality: A Difficult Balance
The dispute highlights the challenge of balancing two important priorities: protecting sensitive company information and maintaining an environment where researchers can raise legitimate safety concerns.
AI companies need strong confidentiality policies to protect proprietary research, security information, and user data. Unauthorized disclosure can create serious risks, particularly when advanced systems and security vulnerabilities are involved.
At the same time, employees need clear guidance on how to report potential safety problems and collaborate with approved external evaluators. If internal policies are unclear or inconsistently communicated, employees may struggle to determine which activities are permitted.
Establishing transparent reporting channels, documented procedures, and independent review mechanisms can help organizations address these competing needs.
The goal should be to protect confidential information without discouraging responsible reporting or legitimate scientific discussion.
What This Means for the Future of AI Development
The controversy comes amid broader discussions about whether AI companies are doing enough to manage the risks associated with increasingly powerful systems.
For technology companies, the situation underscores the importance of creating workplace policies that clearly distinguish between unauthorized information sharing and good-faith safety research.
It also raises questions about how organizations should handle disagreements between researchers and management, particularly when those disagreements concern potential risks to users or the public.
Clear escalation procedures, consistent enforcement of policies, and appropriate independent oversight can help maintain trust between researchers and company leadership.
For the wider AI industry, the case illustrates why responsible development requires more than technical improvements. Strong governance, accountability, and effective communication are also essential.